Make access and accountability part of your software.
Identity, access control, and audit logging built into the applications you already run — reviewed and implemented by an independent engineering team.
For teams improving application identity, access, auditability and controls.
When this service helps
Access that outgrows your app
As users, roles, and tenants multiply, ad-hoc permission checks become hard to reason about and easy to get wrong.
Unclear security and compliance risk
You need to reduce the risk of unauthorized access and gaps, but it is not obvious where the weaknesses are or what to fix first.
Operational and regulatory expectations
Customers, partners, or regulators ask for access controls and audit evidence your current software cannot yet produce.
What we can help with
Secure Software Architecture
Design applications with identity, access, and data boundaries considered from the start.
Authentication & Authorization
Verify who a user is, then enforce what that user is allowed to do — as distinct layers.
SSO & Enterprise Identity
Connect your app to a central identity provider for single sign-on and managed accounts.
Role-Based Access Control
Model roles, permissions, and tenant boundaries so access maps to real responsibilities.
Audit Logging
Record access decisions and sensitive actions so activity can be reviewed and explained.
Application Security
Find and fix application-level weaknesses in code, dependencies, and configuration.
Compliance-Readiness Engineering
Build the controls and evidence that help you prepare for a formal assessment.
From identity to accountable access
A simple view of how a request is authenticated, authorized against role and tenant, and recorded — whether it is allowed or denied.
A request is first authenticated to verify identity, then checked for authorization against the user’s role and tenant — two distinct steps. An allowed request proceeds to an authorized action; a denied request returns a refusal. Both outcomes write an entry to the audit log, so every access decision stays accountable. This illustrates access controls and audit records; it is not a certification claim.
You provide
- Your systems and user roles
- Current access and requirements
- Decisions on policy
We handle
- Identity, permissions, and sign-in
- Access reviews and controls
- Audit logging
You receive
- Role-based access you can explain
- An audit trail of who did what
- Documentation and recommendations
How we work
- 1
Assess risk
Review your application’s identity, access model, and audit gaps against the risks that matter to you.
- 2
Agree controls
Confirm the authentication, authorization, logging, and hardening changes to make — with your sign-off on scope.
- 3
Implement and test
Build the agreed controls and test that allowed and denied paths, roles, and tenants behave as intended.
- 4
Review
Walk through the results and evidence with your team and agree any follow-up or handover.
What you receive
Risk and control findings
A clear review of your current identity, access, and audit posture, and the gaps we recommend closing.
Scoped security changes
The confirmed authentication, authorization, logging, and hardening work we will implement.
Verification evidence and guidance
Test results, audit-log examples, and operational guidance for running the controls day to day.
People responsible for delivery
Illustrative delivery roles for this service — not named staff or promised staffing. Your team is defined in the proposal.
Leads the risk review and designs the authentication, authorization, and audit controls.
Implements the controls inside your application and verifies allowed and denied behavior.
Owns scope, review checkpoints, and handover, and keeps your team aligned throughout.
Track progress, review changes, and stay aligned through your project portal — projects, milestone progress, published updates, approvals, billing, and messages in one place.
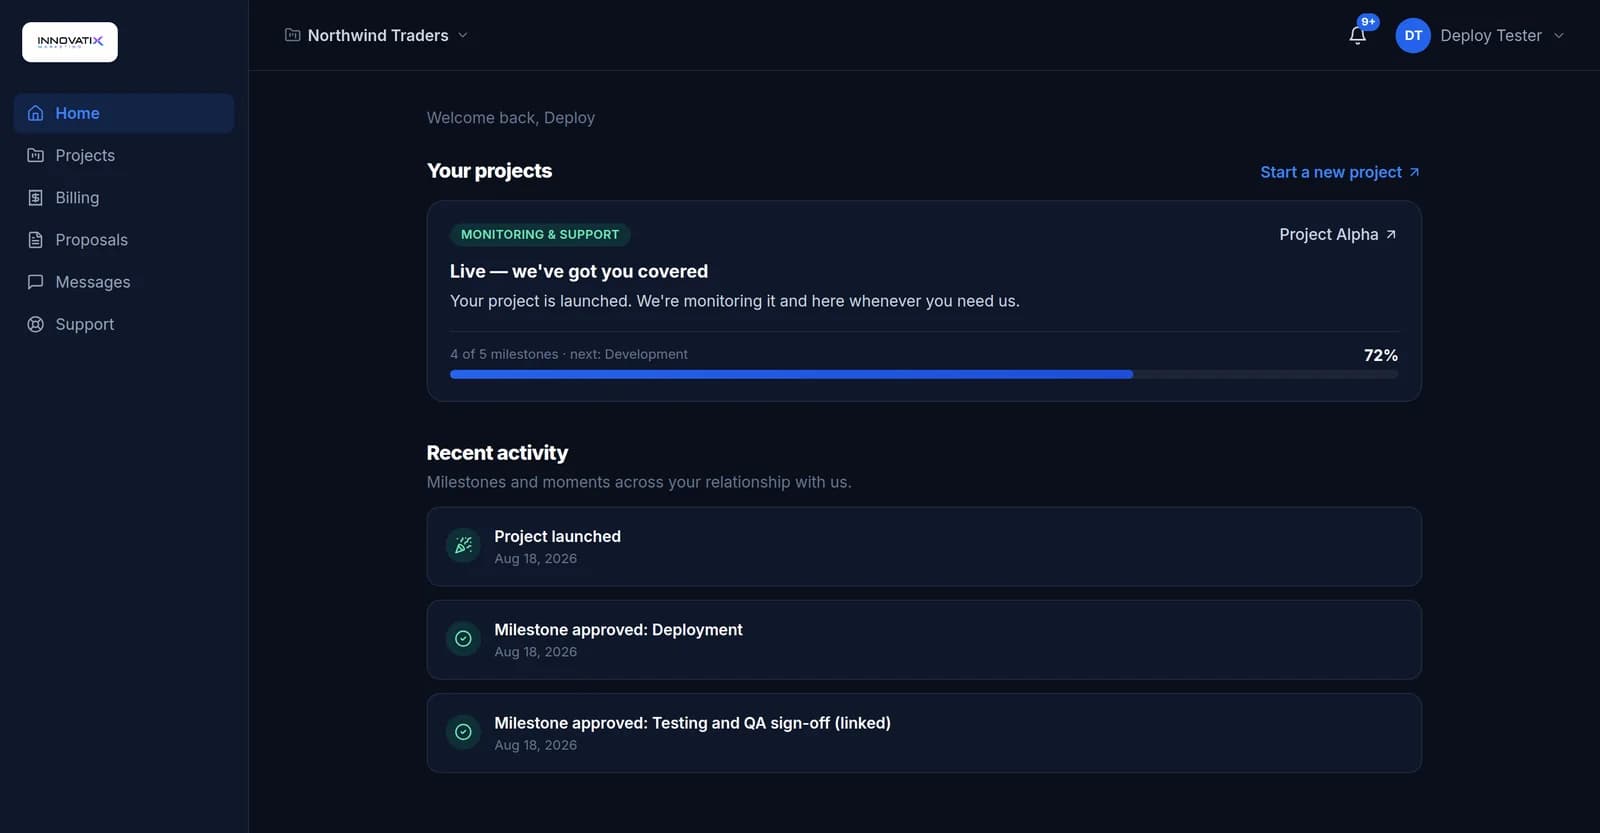 Client portal · demo
Common questions
- Is certification included?
- No. We engineer controls and produce evidence to help you prepare, but a formal certification or attestation is a separate assessment, usually carried out by an independent auditor. We do not issue or promise certification.
- Can you work with our existing software?
- Usually yes. We start by agreeing the review scope for the application as it is today, assess the current identity and access model, and recommend changes before implementing anything.
- Do you need our production credentials or user passwords?
- No. We work through delegated access at the permission level the task needs, against non-production environments where possible, and never collect user passwords or payment credentials through the inquiry form.
- Assessment scope — the application and environments to review
- Identity provider or current sign-in method
- User roles and permission model
- Tenant boundaries and data separation needs
- Required evidence and who is responsible for each control
Tell us where access and auditability need to improve.
Let’s review your application’s identity, access controls, and audit needs together.