Compliance-Readiness Engineering
We engineer the technical controls and documentation that support your path toward a compliance program you pursue separately.
- Access, logging, and encryption control setup
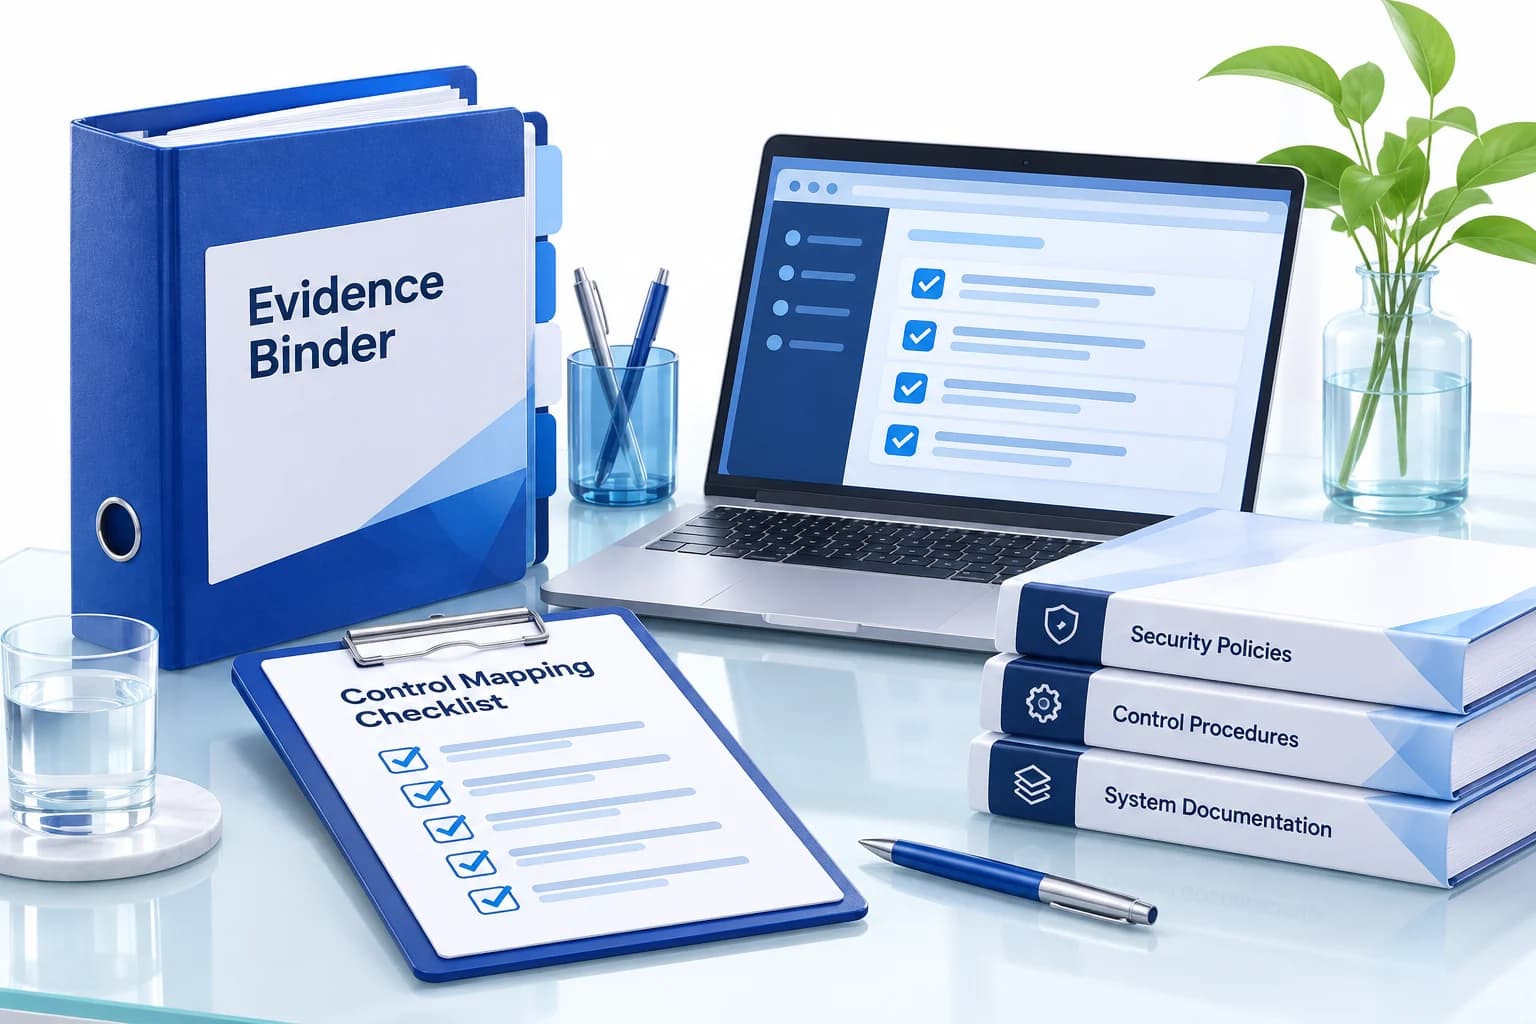
- Evidence and control-mapping documentation
- Supports your auditor; we do not certify
Problems we solve
Enterprise deals stall on security review
A large customer’s security questionnaire asks for controls you have not built, and the deal stalls. Readiness is a revenue issue, not just a compliance one.
Controls exist but there is no evidence
Auditors need proof, not promises. Without audit logs and documented controls, even a secure system fails the review.
Compliance treated as a document exercise
Policies without technical enforcement do not protect anyone and do not survive scrutiny. The controls have to be real in the software.
The workflow
You provide
- Target framework or standard
- Current controls and docs
- System owners
We handle
- Control mapping
- Evidence collection
- Gap analysis
You receive
- Control-to-evidence map
- Documented gap list
- Audit-readiness summary
How we approach it
Compliance frameworks like SOC 2 and HIPAA are, at the technical level, a checklist of controls: least-privilege access, audit trails, encryption, secure change management, and the evidence to prove them. We do not sell certifications — we build the engineering that makes passing them straightforward.
We assess your systems against the controls that matter, close the gaps, and put the evidence-generating machinery in place, so an audit or a big customer’s security review becomes a confirmation rather than a scramble.
Map controls to your systems
We translate the relevant framework (SOC 2, HIPAA-aligned) into concrete technical controls and assess where your systems already meet them and where they do not.
Engineer the missing controls
Least-privilege access, audit logging, encryption in transit and at rest, secure change management, and monitoring — built into the software, not bolted-on policy.
Generate the evidence
The audit trail, access reports, and documentation that reviewers ask for, produced by the system so evidence is a query, not a fire drill.
What you get
- A controls gap assessment against your target framework
- Least-privilege access and RBAC enforcement
- Audit logging and access/change evidence
- Encryption in transit and at rest, secrets management
- Secure change management (CI/CD, reviews, backups)
- Documentation and audit-evidence runbooks
Technologies & integrations
Our delivery process
- 01Scope
Identify the target framework and applicable controls.
- 02Assess
Gap-check current systems against those controls.
- 03Engineer
Build the missing technical controls.
- 04Evidence
Wire up audit trails and reporting.
- 05Document
Produce runbooks for the audit/review.
Frequently asked questions
Do you provide the actual certification or audit?
No — certification is issued by an accredited auditor. We build and document the technical controls and evidence so the audit goes smoothly; we can coordinate with your chosen auditor.
Which frameworks do you support?
We focus on the common technical control sets — SOC 2 and HIPAA-aligned engineering — which overlap heavily with what enterprise security reviews demand.
We are early — is this premature?
The highest-value controls (access, audit logging, encryption, backups) are good engineering regardless, and building them early is far cheaper than retrofitting under deal pressure.