SSO & Enterprise Identity Integration
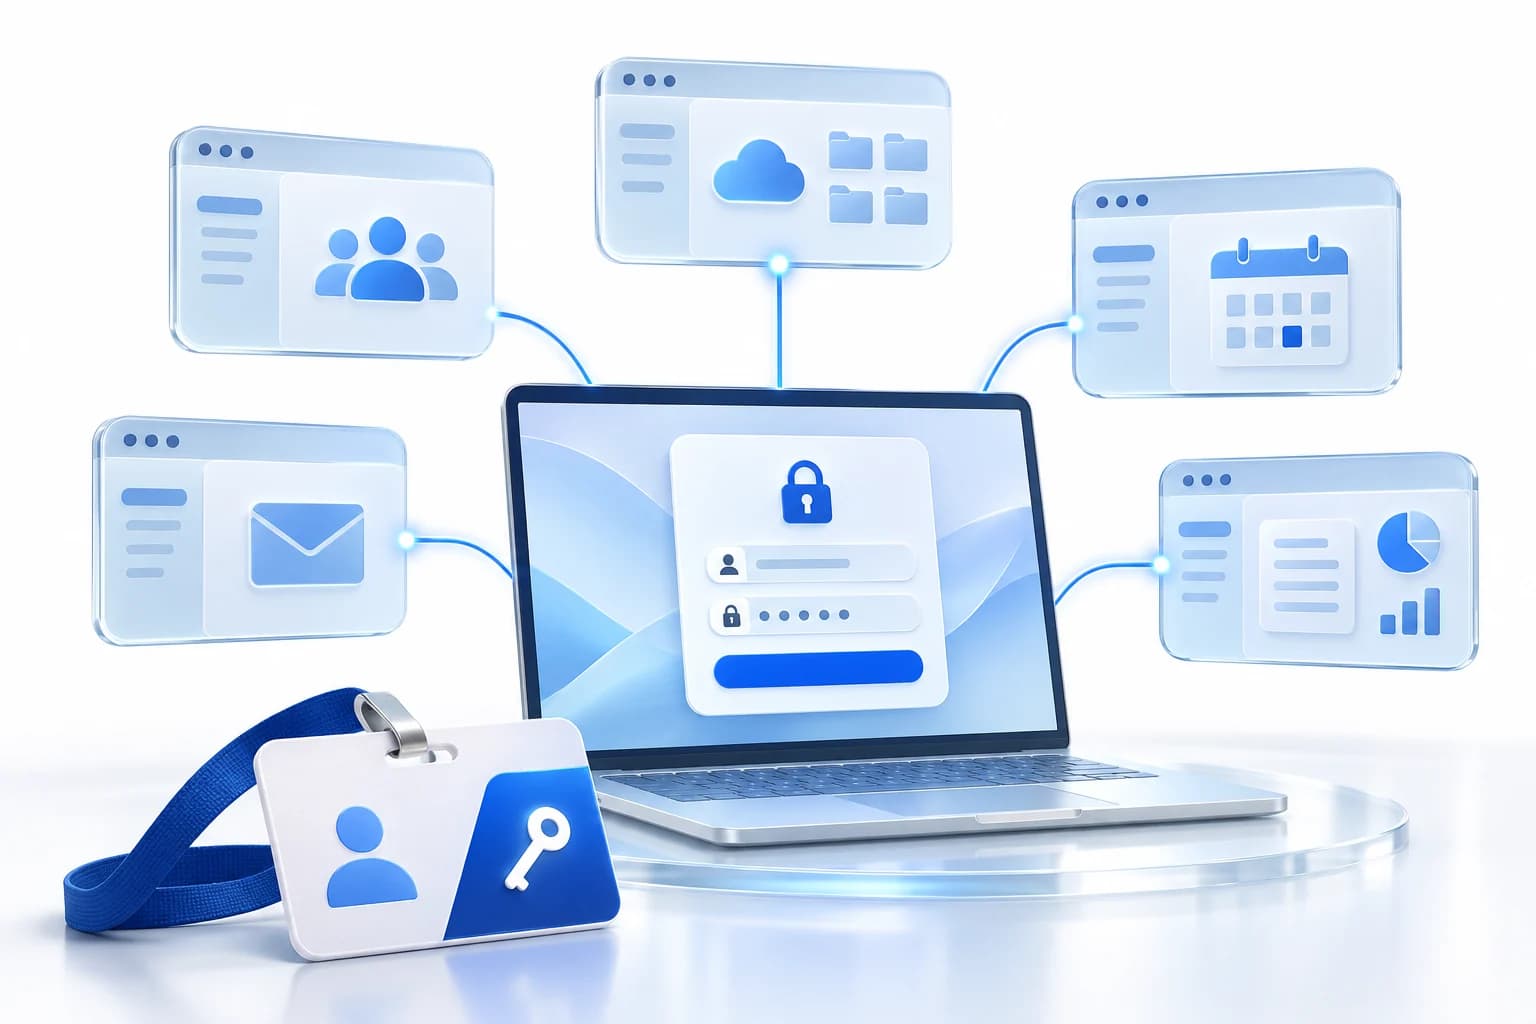
We connect your apps to corporate identity providers via SAML or OIDC so staff sign in with existing company accounts.
- SAML / OIDC provider integration
- User provisioning and group-to-role mapping
- Scoped to providers you already license
Problems we solve
Access that outlives employment
Without central identity, a departing employee’s scattered logins linger, each a standing risk. SSO makes revocation a single action.
Password sprawl
Separate credentials per app mean weak, reused passwords and constant reset tickets. One federated identity fixes both.
No central visibility of access
When each app manages its own users, no one can answer "who can access what" — a problem for security and for audits.
The workflow
You provide
- IdP metadata and endpoints
- User attribute mapping
- Target applications
We handle
- SAML or OIDC wiring
- Claim and role mapping
- Provisioning setup
You receive
- Working SSO connection
- Attribute mapping config
- Rollout checklist
How we approach it
When a business grows, managing a separate login for every application becomes a security and support burden. Single sign-on lets employees use one enterprise identity everywhere, and lets IT grant and revoke access centrally — including the moment someone leaves.
We integrate your applications with enterprise identity providers over SAML and OIDC, with role mapping and provisioning, so access is centralized, auditable, and instantly revocable.
Federated login over SAML / OIDC
We integrate with Okta, Azure AD/Entra, Google Workspace, and other IdPs so users authenticate once with their enterprise identity.
Role mapping and provisioning
Group and role claims from the IdP map to application roles, and provisioning/de-provisioning keeps access in sync automatically.
Central control and revocation
Access is granted and revoked centrally at the IdP, so offboarding is immediate and "who can access what" has a single answer.
What you get
- SAML/OIDC integration with your identity provider
- Role/group claim mapping to application permissions
- Just-in-time or SCIM-style provisioning where supported
- Central revocation and offboarding flow
- Fallback and break-glass access handling
- Documentation and configuration handover
Technologies & integrations
Our delivery process
- 01Assess
Identify the IdP, apps, and role mapping requirements.
- 02Integrate
Wire SAML/OIDC login into the applications.
- 03Map roles
Translate IdP groups/claims into app permissions.
- 04Provision
Automate access sync and offboarding.
- 05Verify
Test login, revocation, and break-glass paths.
Frequently asked questions
Which identity providers do you support?
The standards-based ones — SAML 2.0 and OIDC — which covers Okta, Azure AD/Entra, Google Workspace, OneLogin, and most enterprise IdPs.
Can access be revoked instantly when someone leaves?
Yes — that is a core benefit. Because identity is centralized at the IdP, disabling the user there revokes access to every integrated app at once.
Do you handle automated provisioning?
Where the IdP supports it, yes — via just-in-time provisioning or SCIM — so accounts and roles stay in sync without manual work.